Showing posts with label hacker. Show all posts

Wednesday, October 26, 2011

ANONYMOUS SAYS IT IS GOING AFTER THREE TARGETS ON NOVEMBER 5TH


November 5, known as Guy Fawkes Day in Britain, is a special day for Anonymous. And this November 5, Anonymous is celebrating by saying it will make three different raids: an attack on the social media giant Facebook, a physical protest against banks, and an assault on right-wing news network Fox News.

In "Operation Facebook", Anonymous is targeting Facebook for their inadequate privacy settings and for “selling information to government agencies and giving clandestine access to information security firms so they can spy on people from all around the world.” There has been some confusion, even on the part of Anonymous if this operation will actually take place. A call-to-arms video was refuted by a tweet by AnonOps, the Twitter stream of Anonymous Operations, only to be partially retracted with another tweet explaining that some members still might partake in the raid.

"Operation Cash Back" or "Operation Cash Run", both names are used for the same thing, was announced two weeks ago via YouTube video, and the call-to-arms has already been duplicated various times. Both are is reminiscent of the “Move Your Money” project, which asks supporters to close down their accounts with large international banks. They also coincide with Bank Transfer Day, a Facebook group with over 25,000 like, which has a similar objective. Operation Cash Run will both strengthen your community and weaken the forces of global corruption” says the modulated anonymous voice in the Operation Cash Run video. The Operation Cash Back video shares a similar message, and even links to the Bank Transfer Day Facebook page.

The third activity is dubbed "Operation Fox Hunt" and is designed to go after Fox News. The first video calls Fox News’ broadcasts “conservative right-wing propaganda” and states that Anonymous is motivated to punish Fox news for “belittling” Occupy movement protesters. “I've always looked at Fox News as publishing news that borderline Libel (the publication of matter in a defamatory manner). It would be nice for someone to show the truth for once and not the skewed version of it” wrote Bolderdash in a supportive comment on a Reddit thread about the video.

At time of publication, Fox News had yet to make a statement regarding the “Operation Fox Hunt” videos.

Tuesday, August 2, 2011

LULZSEC HACKER JACK DAVIS, AKA TOPIARY, RELEASED ON BAIL


District Judge Howard Riddle released 18-year old alleged LulzSec hacker Jack Davis on bail Monday morning. Davis hacked under the name “Topiary” online and served as the public face of LulzSec, often publishing press releases and status updates on the group’s Twitter account, before he was arrested on July 27th. The news debunks earlier reports thatauthorities had been duped into arresting an the wrong man.

Authorities in the U.K. said they discovered personal information for more than 750,000 people on Davis’ computers. Davis has been charged with hacking the Sun, Times, Sony and the Serious Organized Crime agency. Davis’ lawyers are highlighting his role as a press secretary for LulzSec and have argued that Davis did not participate in the attacks directly. Davis was released on bail but cannot access the Internet from any device, including from smartphones, The Financial Times said.

Thursday, July 28, 2011

LULZSEC 'TOPIARY' ARRESTED


The Metropolitan Police Service announced on Wednesday that it has arrested a 19-year old hacker suspected to be a member of both “Anonymous Operations” and “Lulz Security,” also known as “LulzSec.” The hacker, who went by the name Topiary, served as the publicist of both hacker groups and often posted press releases and statements on Twitter. His apartment in the Shetland Islands, Scotland is currently being searched and Topiary is on his way to a police station in London. A second 17-year old person in Lincolnshire, England is also being interviewed but has not yet been arrested. The FBI began raiding apartments and arresting a number of people believed to be involved with Anonymous and LulzSec on July 19th. The hacker groups responded to the arrests and said there is “nothing – absolutely nothing – you can possibly to do make us stop.” During that time, Topiary is believed to have tweeted “Arresting people won’t stop us, FBI. We will only cease fire when you all wear shoes on your heads. That’s the only way this is ending,” from the official LulzSec Twitter account.

Wednesday, July 27, 2011

APPLE LAPTOPS CAN BE HACKED TO EXPLODE


Apple’s newer MacBook, MacBook Air and MacBook Pro notebooks have a security flaw that can allow hackers to remotely prevent the batteries from charging. Better yet, hackers can exploit the same flaw and remotely cause batteries to explode. Apple laptops’ new “smart” battery technology is intended to provide added control over power management, and it does just that. Unfortunately, it also gives hackers added control because the microcontroller chip that ships in recent Apple laptops can be accessed remotely using a default password shared by each and every notebook.

Charlie Miller, the security expert who discovered the vulnerability, plans to showcase the flaw next month at the Black Hat security conference. There, Miller will show that he is able to access the battery controller remotely and cause it to refuse a charge, or even heat up until it catches fire and explodes. “These batteries just aren’t designed with the idea that people will mess with them,” Miller told Forbes last week. “What I’m showing is that it’s possible to use them to do something really bad.” Thankfully, the security expert also intends to showcase a fix for the flaw, which Apple will hopefully implement as soon as possible.

Friday, June 24, 2011

HACKER PLEADS GUILTY IN AT&T iPAD BREACH


Nearly six months after his arrest, one hacker pleaded guilty to charges that he exposed the email addresses of over 100,000 AT&T iPad 3G users. It's been a year since Daniel Spitler and his compatriot, Andrew Auernheimer, coaxed Ma-Bell servers into delivering the goods, with a brute force script they lovingly named the iPad 3G Account Slurper. The hacker's plea agreement suggests a 12 to 18-month sentence, which is a lot more lenient than the 10-year maximum we hear he could face. Spitler's collaborator is apparently still in plea negotiations with the prosecutor. Both men initially claimed they were just trying to draw attention to a security hole, but maybe next time they'll think twice before embarking on such altruistic endeavors.

Wednesday, June 22, 2011

LULZSEC DENIES LEADER ARRESTED


There are numerous reports claiming that the leader of the now infamous hacking group LulzSec has been arrested in the United Kingdom. According to London’s Metropolitan Police, the shadowy leader was a 19-year old responsible for hacking “a number of international businesses and intelligence agencies.” The group took responsibility for Sony’s recent massive security breach and has also targeted a number of high-visibility websites, including that of the Central Intelligence Agency, and has waged war on the U.S. government with another group dubbed Anonymous.

Despite the reports, however, LulzSec has denied that any of its members have been arrested. Early Tuesday morning the group tweeted: “Seems the glorious leader of LulzSec got arrested, it’s all over now… wait… we’re all still here! Which poor bastard did they take down?”

Friday, June 10, 2011

MICROSOFT HIRES 14-YEAR OLD MODERN WARFARE HACKER


A 14-year-old Irish school boy known only as Jake managed to hack into the Xbox 360 servers for Modern Warfare 2 and cause a phishing scam alert .

It wasn’t big news as Microsoft handled it, but they wanted to know what had caused it and if it was related to the PSN hacking incident. They managed to trace it back to this Irish schoolkid, which must have come as a bit of surprise. It’s not every day someone so young can learnt he skills to find an exploit and then do the work to gain access to such a system.

To give Microsoft credit where it’s due, they didn’t turn on the boy. Instead, they have decided to make him their youngest employee. The thinking being, he is obviously adept and Microsoft want to nurture that talent. Who knows, he could be the next Bill Gates.

Working with Microsoft in Ireland, managing director of the division Paul Rellis said they aim to, “develop his talent for legitimate purposes.”

Wednesday, April 27, 2011

PLAYSTATION NETWORK HACKED, PERSONAL INFORMATION STOLEN


On Tuesday, Sony issued an update explaining the recent PlayStation Network and Qriocity outages. The company said it has discovered that between April 17th and April 19th, someone broke into its network and stole user information. In an effort to stop the security breach, Sony temporarily killed access to its PlayStation Network and Qriocity services, hired a security firm to investigate, and started beefing up its security measures. However, the leaked information may be alarming to PlayStation network users. Here’s part of Sony’s statement:
We believe that an unauthorized person has obtained the following information that you provided: name, address (city, state, zip), country, email address, birthdate, PlayStation Network/Qriocity password and login, and handle/PSN online ID. It is also possible that your profile data, including purchase history and billing address (city, state, zip), and your PlayStation Network/Qriocity password security answers may have been obtained.
Sony said that it doesn’t think credit card data was taken, but that it will not rule out the possibility, and says that it’s possible credit card numbers – excluding the security codes – may have been obtained by the intruders. The firm advises that its customers “remain vigilant” by closely monitoring credit statements. Sony says the services will be reactivated as soon as possible and that customers can dial 1-800-345-7669 with any questions.

Thursday, February 17, 2011

SONY PLAYSTATION 3 TRANSMITS CREDIT CARD INFORMATION IN THE CLEAR

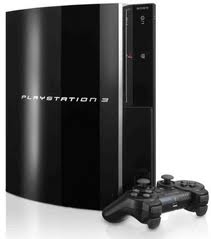
Sony has just officially announced that anyone who hacks their PlayStation 3 will find themselves (and not merely the hacked PS3) banned for life from the PlayStation Network. How does Sony know that you’ve hacked your console, though? After all, a PS3 hacked with the released master key should be virtually indistinguishable from a non-hacked machine, at least from a systems perspective.

The answer, at least according to one hacker, is that Sony collects a lot of data about users when they log into the PlayStation Network. Even worse than the volume of data collected — which is all automatically transferred to Sony when your PS3 connects to your WiFi network — is the way it is transmitted: in plain-text, with absolutely zero encryption.

“Sony is the biggest spy ever… they collect so much data. All connected devices return values sent to Sony’s servers,” the hacker said. According to him, Sony knows literally everything about your PlayStation 3, including which controllers you’re using, what USB devices are plugged in, what television is hooked up to it, everything.

Most alarming? This is the way Sony transmits your credit card information for every purchase:
creditCard.paymentMethodId=VISA&creditCard.holderName=Max&creditCard.cardNumber=45581234567812345678&creditCard.expireYear=2012&creditCard.expireMonth=2&creditCard.securityCode=214&creditCard.address.address1=example street%2024%20&creditCard.address.city=city1%20&creditCard.address.province=abc%20&creditCard.
That’s not unencrypted. That’s literally how the PS3 transmits your credit card information to its servers. That means that if you’re on an uncompromised network, literally anyone can pluck your credit card information from the air and use it for whatever he wants.

The hacker also states that the reason Sony is going on the offense when it comes to the PlayStation Network is because the release of the PS3 master key now makes it possible for anyone with a hacked PS3 to download as much content from the PSN Store as they want, all for free.

Perhaps this explains why Sony has been going to such lengths to sue, silence or hide all details of the PS3 jailbreak: they know their system is a security liability and now that it’s been blown wide open, they fear massive fraud and class-action lawsuits from the defrauded.

Tuesday, February 8, 2011

SONY INCREASES PRESSURE ON GEORGE HOTZ, AKA GEOHOT, DRAGS YOUTUBE INTO THE FRAY


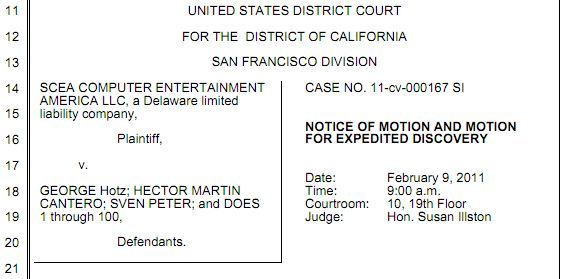
Now that Sony has started gathering the evidence it needs via discovery in the lawsuit over Hotz and friends' PS3 jailbreak, the company has dropped a hammer by moving to reduce the amount of time the hackers have to get Sony the information it wants. Sony filed the motion -- which will be heard by the court tomorrow -- to better arm itself with information to oppose Geohot's motion to dismiss, scheduled to be heard in early March. Casting its evidence-gathering net far and wide, SCEA has demanded that YouTube surrender not only information for Hotz's account where his jailbreak video was posted, but also how many users accessed the video, the usernames of those with access to the video, and all usernames and IP addresses of everyone who posted or published comments to the vid. In addition to hitting up YouTube for dirt, Wired reports that Sony has demanded Twitter hand over the personal info of fail0verflow's members -- we're waiting for Sony's lawyers to don TSA gear as the next step in their search. Geohot's attorney thinks the requests seem a bit much, but we think they make sense given Sony's strategy of going after the entire fail0verflow team. While these goings-on make for fairly standard legal tactics, they won't do much for Sony's public image.

Saturday, February 5, 2011

NASDAQ COMPUTERS INVADED BY HACKERS


According to the Wall Street Journal hackers have repeatedly penetrated the computer network of the company that runs the Nasdaq Stock Market during the past year, and federal investigators are trying to identify the perpetrators and their purpose, according to people familiar with the matter.

The exchange's trading platform—the part of the system that executes trades—wasn't compromised, these people said. However, it couldn't be determined which other parts of Nasdaq's computer network were accessed.

Investigators are considering a range of possible motives, including unlawful financial gain, theft of trade secrets and a national-security threat designed to damage the exchange.
The Nasdaq situation has set off alarms within the government because of the exchange's critical role, which officials put right up with power companies and air-traffic-control operations, all part of the nation's basic infrastructure. Other infrastructure components have been compromised in the past, including a case in which hackers planted potentially disruptive software programs in the U.S. electrical grid, according to current and former national-security officials.
"So far, [the perpetrators] appear to have just been looking around," said one person involved in the Nasdaq matter. Another person familiar with the case said the incidents were, for a computer network, the equivalent of someone sneaking into a house and walking around but—apparently, so far—not taking or tampering with anything.

A spokesman for Nasdaq declined to comment.

Dogster/Catster

Saturday, January 29, 2011

SONY RELEASES UPDATE FOR PS3; HACKERS PROMPTLY CRACK IT


Sony has released an update to the PS3, bringing the firmware to version 3.56. The firmware update was designed to close the security hole in the PS3 that allowed hackers to obtain the master key and allow them to run any code on the console.

Unfortunately, within hours of the update being released, hackers were able to crack it and open the consoles up once again. The problem is that the master key is out on the internet for anyone to find and use. Sony can't stop this without producing new hardware and then it still has all the original consoles to deal with.

With the master key hackers have the ability to anything they want on the consoles, allowing them to cheat at online games and play games for free potentially taking money out the pockets of game developers.

Winter Sale - Save up to 88% off

Tuesday, December 14, 2010

MCDONALDS WEBSITE HACKED; RONALD NOT HAPPY


According to Reuters, McDonald’s Corp has just announced that hackers gained access to a database containing an unidentified number of email address and birthdates for the strange breed of person who goes to McDonald’s’ websites and decides to subscribe.

On the one hand, the hack is less invasive than the Gawker hack, because it doesn’t appear that passwords were compromised. On the other hand, McDonald’s is being cagey about the actual numbers of customers involved… and while credit card numbers, passwords and social security numbers were not compromised, birthdays were… making it possible on some sites for those email addresses to be paired with birthday security questions.

Gawker and McDonald’s aren’t the only huge breaches in the last week. On Friday, Walgreens admitted that one of their databases containing customer email addresses had been breached as well. [Geek]


65% Off GPS Platform 3.5 TFT LCD $44.99 (Regular Price 129.99)

Friday, October 29, 2010

REAL HACKER FACT CHECKS 'THE GIRL WHO KICKED THE HORNETS NEST'

Vanity Fair has an interview with a reformed hacker Kevin Poulsen, specifically about the hacking Lisbeth Salander does in the blockbuster best selling books by Stieg Larsson The Girl with the Dragon Tattoo, The Girl Who Played with Fire and The Girl Who Kicked the Hornet's Nest. 


Poulsen, a former "black hat" hacker who's now the editor of Wired.com's Threat Level, says that as far as fictionalized hacking goes, Lisbeth Salander's cyber conquests are pretty realistic, even if the way she goes about doing them are a bit fuzzy:

Michael Hogan: Is there anything that Lisbeth Salander did that struck you as implausible?
Kevin Poulsen: The interesting thing is, everything that she does is completely plausible-it's the way she does it that is for the most part completely nonsensical as a technical matter.
MH: Can you explain?
KP: Well, she uses a device given to her by her other hacker buddy-she puts it over the co-ax cable of the corrupt financier, Hans-Erik Wennerström. The entire description of how that works and how she uses it to get control of his computer is just a fabrication. She describes taking his computer and basically setting it up so that when this guy thinks he's logged in using his computer, he's actually using her server-and she's able to monitor everything.
MH: Right.
KP: That isn't how it would be done. But you certainly are seeing these days attacking somebody's P.C. instead of attacking their server, and logging their key strokes and all of that. This is exactly what the hackers are doing right now. That's what they are doing in financial crimes in particular. When you get down to the technical details, it's all very fictional. But the actual capabilities are all completely real.

Interesting...I'm now going to run my anti-virus, scanners and any other security software I can find! [Gizmodo] [Vanity Fair]

gay-blog-member-of-the-best-gay-bloggers